LIVE
TRACECHAIN™FORENSICS
FRAUD INTELLIGENCE · CASE FILES · GLOBAL SCOREBOARD
REPORT FRAUD Find your country and who to contact ▸🔍 Search cases, companies, countries, agencies
INTEL
PIG BUTCHERING: now the #1 loss category in the US by estimated volume / HUSHPUPPI: the Instagram that became the evidence -- Case 001 open / BEC: one spoofed email, one wire, seven figures -- see the methodology / ROSS ULBRICHT: full pardon January 21 2025 after 11+ years -- Case 013 open / ALL FIGURES LABELED: estimate vs conviction vs market collapse -- see Methodology / UNODC 2023: $5.4B estimated annually from SE Asia pig-butchering compounds [UNVERIFIED] / PIG BUTCHERING: now the #1 loss category in the US by estimated volume / HUSHPUPPI: the Instagram that became the evidence -- Case 001 open / BEC: one spoofed email, one wire, seven figures -- see the methodology / ROSS ULBRICHT: full pardon January 21 2025 after 11+ years -- Case 013 open / ALL FIGURES LABELED: estimate vs conviction vs market collapse -- see Methodology / UNODC 2023: $5.4B estimated annually from SE Asia pig-butchering compounds [UNVERIFIED]
COMPANY · GROUP/MALWARE

REvil (Sodinokibi)

🇷🇺 Russia · FOUNDED 2019-04
THE FIGURE
$200M+
Ransom payments the DOJ attributes to REvil/Sodinokibi across ~175,000 infected computers (November 2021); Vasinskyi's own restitution order is ~$16M.
WHAT IT SAID IT WAS

A Russian-speaking ransomware-as-a-service operation that succeeded GandCrab in 2019, with a 'Happy Blog' leak site and affiliates who kept 70–80% of ransoms.

WHAT IT REALLY WAS

The gang behind the 2021 JBS ($11M paid) and Kaseya attacks (~1,500 businesses, $70M demanded); the DOJ says its victims paid over $200M in ransoms.

THE STORY

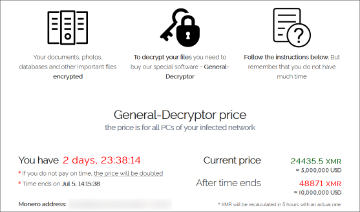
REvil surfaced in April 2019 as the successor to GandCrab and became the most aggressive ransomware franchise of the pandemic years, extorting JBS for $11 million in June 2021 and, on 2 July 2021, pushing ransomware through Kaseya's management software to some 1,500 businesses with a $70 million demand. Its sites went dark days later; when they returned in September, a US-led operation hacked and shut the servers in October 2021. Yaroslav Vasinskyi, arrested at the Polish border, was extradited and sentenced to 13 years 7 months in May 2024. Russia's FSB arrested 14 alleged members on 14 January 2022, the group's effective end.

WHO RAN IT
Yaroslav Vasinskyi ▸
affiliate ('Rabotnik'); ran the Kaseya attack · open the case file
Yevgeniy Polyanin
affiliate — indicted November 2021; $6.1M seized; at large
'UNKN' (Unknown)
public spokesman/administrator — disappeared July 2021; unidentified
WHO WAS HURT
Kaseya and ~1,500 downstream businessesJBSAcerQuanta ComputerTravelexhundreds of others
HOW IT ENDED
Founded
2019-04
Based
Russia
Ended
2022-01-14
How
dismantled — servers hacked offline by a US-led operation October 2021; 14 members arrested by Russia's FSB 14 January 2022

DOJ seized $6.1M in ransom proceeds from affiliate Yevgeniy Polyanin (November 2021). Vasinskyi extradited from Poland: 13 years 7 months and $16M restitution (May 2024). FSB arrested 14 in January 2022; a St Petersburg court gave four of them 4½–6 years in October 2024. Ukrainian affiliate arrests in Operation GoldDust (November 2021).

SOURCES
en.wikipedia.org/wiki/REviltherecord.media/fsb-raids-revil-ransomware-gang-members
Facts as published in court records, regulator releases and the sources above. Anyone charged and not convicted is alleged only.
🏠 HOME📁 CASES🚨 WANTED🎮 PLAY🌍 WORLD