Hive ransomware
A ransomware-as-a-service operation active from June 2021, renting its malware to affiliates and running a leak site.
A gang that hit more than 1,500 victims in 80+ countries — hospitals, school districts and critical infrastructure — and collected over $100M in ransoms before the FBI secretly infiltrated it.
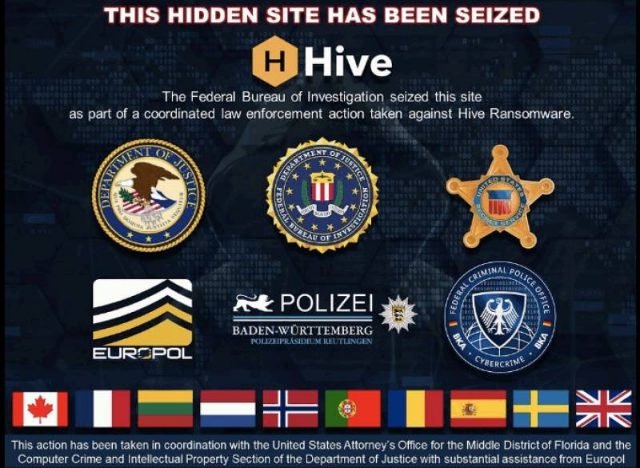
Hive appeared in June 2021 as a ransomware franchise whose affiliates broke into hospitals, schools and utilities, encrypted their systems and threatened leaks; within 18 months it had 1,500 victims and over $100 million in ransoms. In July 2022 the FBI quietly penetrated its network and began handing decryption keys to victims, saving them about $130 million, then seized the servers and leak site on 26 January 2023 with German and Dutch police. Affiliate Mikhail Matveev, charged in May 2023, is in Russia, where he was himself charged in 2024.
FBI captured Hive's decryption keys and handed them to 300+ victims, averting ~$130M in ransoms; sites seized with German and Dutch police. Matveev was indicted in May 2023 for Hive, LockBit and Babuk attacks with a $10M reward; Russia charged him with creating malware in November 2024.