LIVE
TRACECHAIN™FORENSICS
FRAUD INTELLIGENCE · CASE FILES · GLOBAL SCOREBOARD
REPORT FRAUD Find your country and who to contact ▸🔍 Search cases, companies, countries, agencies
INTEL
PIG BUTCHERING: now the #1 loss category in the US by estimated volume / HUSHPUPPI: the Instagram that became the evidence -- Case 001 open / BEC: one spoofed email, one wire, seven figures -- see the methodology / ROSS ULBRICHT: full pardon January 21 2025 after 11+ years -- Case 013 open / ALL FIGURES LABELED: estimate vs conviction vs market collapse -- see Methodology / UNODC 2023: $5.4B estimated annually from SE Asia pig-butchering compounds [UNVERIFIED] / PIG BUTCHERING: now the #1 loss category in the US by estimated volume / HUSHPUPPI: the Instagram that became the evidence -- Case 001 open / BEC: one spoofed email, one wire, seven figures -- see the methodology / ROSS ULBRICHT: full pardon January 21 2025 after 11+ years -- Case 013 open / ALL FIGURES LABELED: estimate vs conviction vs market collapse -- see Methodology / UNODC 2023: $5.4B estimated annually from SE Asia pig-butchering compounds [UNVERIFIED]
Evgeniy Bogachev~$100M+
#67 OF 102

Evgeniy Bogachev

INDIVIDUALBORN IN 🇷🇺 RUSSIA ▸
CASE 059 · RANSOMWARECHARGED
GameOver Zeus · indicted 2014 · fugitive
~$100M+
WHAT WAS TAKEN
Losses the FBI attributes to the GameOver Zeus botnet (alleged); the botnet's, not his.
HOW
Ran a million-computer botnet that stole bank logins, then spread CryptoLocker, the first big ransomware paid in bitcoin, per the FBI.
AT A GLANCE
Known as
slavik
Aliases
slavik · lucky12345 · Pollingsoon
Born
Oct 28, 1983 · Anapa, Russia
Status
Fugitive; believed in Russia
Court
US District Court, Western District of Pennsylvania (14-count indictment unsealed 2 June 2014)
Charges
Conspiracy · Computer hacking · Wire fraud · Bank fraud · Money laundering (14 counts)
Photo: FBI
Story
TAP TO READ FULL NARRATIVE — GAMEOVER ZEUS (500 WORDS)
Sources: DOJ — indictment of Evgeniy Bogachev, June 2, 2014 · FBI — reward and GameOver Zeus materials · Europol/FBI — Operation Tovar, June 2014. STATUS: FUGITIVE. Indicted in 2014, never tried, believed to be in Russia. Bogachev is historically significant as the alleged operator of CryptoLocker — the first widely deployed ransomware to demand payment in cryptocurrency. $3M reward = one of the largest offered for a cybercriminal at that time. Defensive level — model and principle; no operational detail.
· PART ONE ·
FROM BANK DRAIN TO RANSOM — THE PIVOT

GameOver Zeus was a banking trojan botnet — a network of infected computers used to steal banking credentials and drain accounts, running from approximately 2011. Its operator, per the FBI and DOJ, was Evgeniy Bogachev, who went by 'slavik' and other aliases. At its peak, the botnet had infected approximately one million machines worldwide. [SOURCE: FBI; DOJ]

The same infrastructure that ran the banking-trojan operation was used to distribute CryptoLocker — a program that encrypted a victim's files and demanded payment in Bitcoin for the decryption key. This is the point where ransomware, as it is understood today, begins: a demand for cryptocurrency in exchange for access to something the victim needs. Every ransomware case that follows — Cases 056 through 060 — traces back to this model.

Over $100 million in losses have been attributed to the GameOver Zeus operation by the FBI. The ransomware operation's losses are counted separately. [SOURCE: FBI] Bogachev's personal take was a share of the criminal proceeds — not the full loss figure.

· PART TWO ·
OPERATION TOVAR — THE DISRUPTION THAT DIDN'T CATCH HIM

In June 2014, Operation Tovar — a coordinated effort by the FBI, DOJ, Europol, and private sector partners — disrupted GameOver Zeus's botnet infrastructure. The operation temporarily cut the connection between infected machines and the botnet's command-and-control systems. The DOJ unsealed Bogachev's indictment on June 2, 2014.

Bogachev was not arrested. He was not in a jurisdiction that would extradite him. He was believed to be in Russia. By the time the takedown was executed, he had been operating criminal infrastructure for years from a location the US could reach legally but not physically.

The FBI offered a $3 million reward for information leading to his arrest and conviction — at the time, one of the largest rewards ever offered for a cybercriminal. Subsequent reporting indicated that Bogachev's botnet was also used to conduct intelligence collection on Ukrainian government communications — suggesting an overlap between criminal cybercrime and Russian state intelligence interests that would become a documented theme in later years. [SOURCE: security researcher reporting; US government characterizations]

He is still at large. As of September 2026, he has been a fugitive for more than twelve years. He is believed to be in Krasnodar, Russia. He has never been tried. No reward has been collected.

VERIFIED SOURCES — ALL CONDUCT ALLEGED UNLESS NOTED
[1] DOJ — indictment of Evgeniy Bogachev, June 2, 2014. All figures per FBI/DOJ.
[2] FBI — GameOver Zeus materials, Operation Tovar, $3M reward.
[3] Europol/NCA — Operation Tovar international coordination.
[4] Krebs on Security / Wired — the most detailed secondary coverage of Bogachev and GOZ.
TO VERIFY Exact birth date (October 28, 1983 commonly cited — verify to primary) · Whether the intelligence-collection allegation appears in official US government documents or only in security research · Current status
Bio
BIO

IDENTITY

NAME
Evgeniy Mikhailovich Bogachev
HANDLES
slavik · lucky12345 · Pollingsoon
BORN
Oct 28, 1983 · Anapa, Russia
THE OPERATION
GameOver Zeus botnet and CryptoLocker ransomware — administrator (alleged)

CASE RECORD

DISRUPTED
June 2, 2014 · Operation Tovar (FBI, Europol, partners)
INDICTED
June 2, 2014 · W.D. Pa. · 14 counts unsealed
REWARD
Feb 24, 2015 · up to $3M
STATUS
Fugitive; believed in Russia
KNOWN AS
slavik
ALIASES
slavik · lucky12345 · Pollingsoon
COURT
US District Court, Western District of Pennsylvania (14-count indictment unsealed 2 June 2014)
CHARGES
Conspiracy · Computer hacking · Wire fraud · Bank fraud · Money laundering (14 counts)
PLEA
None — fugitive since 2014, believed in Russia
SENTENCE
None
COMPANY
GameOver Zeus botnet and CryptoLocker ransomware — administrator, per the FBI
Timeline
CASE TIMELINE
2011
GameOver Zeus
Banking botnet in operation.
SOURCE: FBI
Sept 2013
CryptoLocker
Ransomware spread through the botnet.
SOURCE: FBI
June 2, 2014
Indicted
Operation Tovar; 14 counts.
SOURCE: DOJ
Feb 24, 2015
$3M reward
FBI.
SOURCE: FBI
Receipts
Pictures and video from the story. Every caption gives when, where and why; tap a name to open that person’s report.
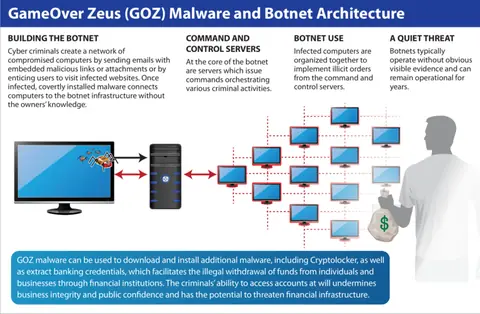
The FBI's own diagram of the GameOver Zeus botnet: infected machines, command-and-control servers, and the CryptoLocker payload
1. The FBI's own diagram of the GameOver Zeus botnet: infected machines, command-and-control servers, and the CryptoLocker payload
2014 (FBI graphic, published with the Operation Tovar announcement) · FBI, Washington, DC
How the operation worked, as the FBI drew it: a network of about a million compromised computers stealing bank logins, then used to push CryptoLocker, which encrypted files and demanded Bitcoin. The model every ransomware case in the series follows.
Graphic: FBI (public domain) · FBI, "GameOver Zeus (GOZ) Malware and Botnet Architecture" graphic (fbi.gov file repository, gameoverzeus_v13_fullgraphic), via Wikimedia Commons File:GameOverZeus_FBI_graphic_(cropped).png
The Justice Department press conference announcing Operation Tovar and the unsealed indictment of Bogachev▶ WATCH
2. The Justice Department press conference announcing Operation Tovar and the unsealed indictment of Bogachev
2 June 2014 · US Department of Justice, Washington, DC
Deputy Attorney General James Cole, with FBI and Criminal Division officials, announced the disruption of GameOver Zeus and CryptoLocker and the 14-count Pittsburgh indictment. Bogachev was not arrested and remains a fugitive.
▶ Watch the video · US Department of Justice (YouTube), 2 June 2014
Video: US Department of Justice; thumbnail via YouTube · The Justice Department (official YouTube channel), "Deputy Attorney General Press Conference for Gameover Zeus and Cryptolocker Operations", 2 June 2014
Operations
Where they were physically based, what they did in each place and when, and the methods they used. Tap a country or a method for its page.
THE MAP
Born in amber; operated from cyan. Tap a marker for the country page.
🇷🇺 Russia — born here
METHODS IN THIS CASE: #39 Banking Trojan — GameOver Zeus botnet stole bank logins (alleged) · #3 Ransomware — CryptoLocker: the first widely paid crypto-ransomware (alleged)
WHAT THEY DID HERE: 2011–2014 — Allegedly administers the GameOver Zeus botnet and CryptoLocker from Anapa on the Black Sea. · 2014–present — A fugitive since Operation Tovar; believed to remain in Russia.
OPERATED FROM
Where they were physically based or worked. Tap a country for its page.
🇷🇺 Anapa, Russia ▸
2011–2014Allegedly administers the GameOver Zeus botnet and CryptoLocker from Anapa on the Black Sea.SOURCE: FBI; DOJ W.D. Pa. (alleged)
2014–presentA fugitive since Operation Tovar; believed to remain in Russia.SOURCE: FBI
Sources
SOURCES
[1] PRIMARY — US DOJ / FBI: GameOver Zeus action and indictment (June 2, 2014)
[2] PRIMARY — FBI: $3M reward (Feb 24, 2015)
More
KEY FACTS
EVGENIY BOGACHEV
GAMEOVER ZEUS · SLAVIK · CASE 059 · RANSOMWARE & MALWARE · INDICTED JUNE 2014 · FUGITIVE
LOSSES
over $100M attributed to the botnet (FBI; alleged)
INFECTED
~1 million computers at the peak (alleged)
REWARD
up to $3M · FBI, Feb 2015
INDICTED
June 2, 2014 · Pittsburgh · 14 counts
CRYPTOLOCKER
The first widely paid crypto-ransomware
STATUS
Fugitive since 2014
INDICTED, NEVER TRIED. $100M is the FBI’s figure for the botnet’s losses, not his take. He is where crypto-ransomware starts, and he has never seen a courtroom.
THE ORIGIN POINT
THE TAKEDOWNJUNE 2014
Operation Tovar
FBI / Europol
Cut the botnet from its controllers; did not catch him.
SOURCE: FBI
HOW IT WORKED

FROM BANK DRAIN TO RANSOM — PRINCIPLE ONLY

01
The botnet: A million infected machines stealing bank logins
02
The pivot: The same machines spread file-encrypting malware
03
The demand: Bitcoin for the key
04
The model: Every ransomware case that followed
WHERE CRYPTO-RANSOMWARE BEGAN
Botnet steals logins
-->
CryptoLocker encrypts files
-->
Bitcoin demanded
-->
Model copied worldwide

WHAT THIS CASE ESTABLISHED

The origin of an industry is a man nobody has arrested.
Series link: Cases 056–058.
🏠 HOME📁 CASES🚨 WANTED🎮 PLAY🌍 WORLD